The Digital Personal Data Protection Act, 2023 now has working rules, and healthcare apps in India have a fixed deadline. MeitY notified the DPDP Rules, 2025 on 13 November 2025. Most substantive duties, including consent notices, security safeguards, breach reporting, retention and data principal rights, apply from 13 May 2027. For a telemedicine or health app, the work is to rebuild consent, logging, breach response and deletion so they meet the Rules before that date.
- 13 November 2025: Rules notified, Data Protection Board provisions in force.
- 13 November 2026: Consent Manager registration opens.
- 13 May 2027: core obligations apply, unless MeitY shortens the timeline.
- Breaches: report to the Data Protection Board within 72 hours and inform affected users without delay.
- CERT-In’s 6-hour cyber incident rule still applies in parallel.
This article is a technical summary, not legal advice. Have a qualified Indian data protection lawyer review your setup.
The DPDP timeline for healthcare apps
The Rules come into force in three phases. A rule-by-rule reference verified against Gazette G.S.R. 846(E) sets out the dates.
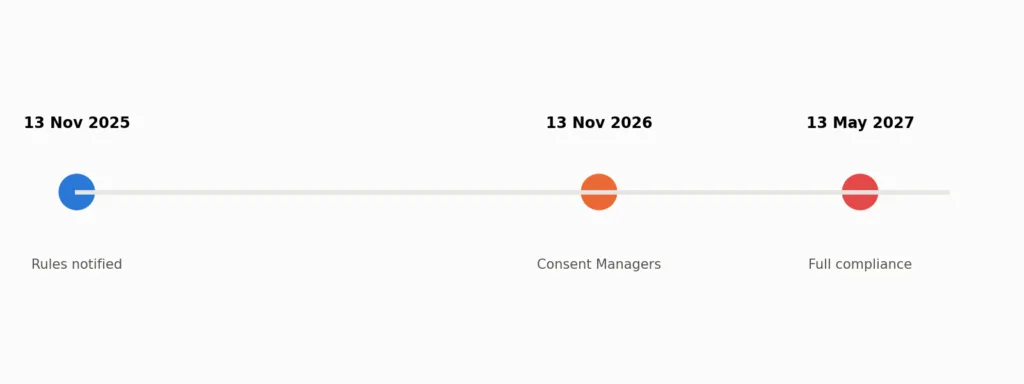
The same source notes that MeitY has floated a proposal to shorten the 18-month window to 12 months, which would move the deadline to 13 November 2026. As of this writing the proposal had not been notified. Plan for the earlier date as a buffer.
Who is who in a health app
The Act uses its own terms. Mapping them to your product is the first step.
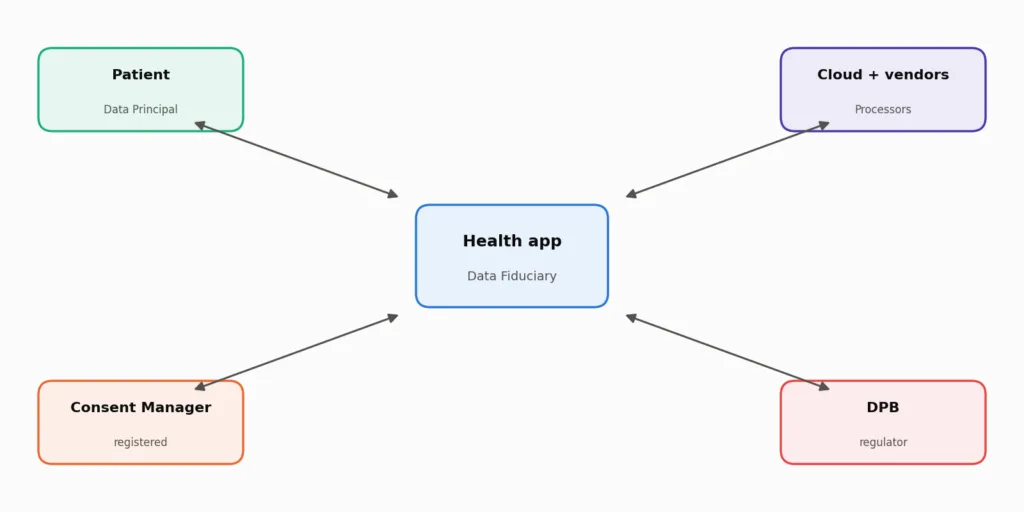
- Data Principal: the patient, or a parent or guardian for a child.
- Data Fiduciary: the clinic, hospital or app company deciding why and how data is processed.
- Data Processors: your cloud provider, video vendor, SMS gateway, analytics tools and labs you pass data to.
- Consent Manager: a registered, interoperable platform people can use to manage consents.
- Data Protection Board of India: the body that handles complaints, breaches and penalties.
Large health platforms may be notified as Significant Data Fiduciaries. EY’s summary of the Rules lists their extra duties: annual data protection impact assessments, audits, algorithmic due diligence and a Data Protection Officer.
DPDP compliance for a health app: the build checklist
1. Consent that stands on its own
The Rules require a notice that stands alone, itemises the data collected and explains the purpose in plain language. For a telemedicine app, separate consents usually make sense for the consultation itself, for sharing records with another provider, for recording, and for any marketing. Store each consent with a version, timestamp and purpose.
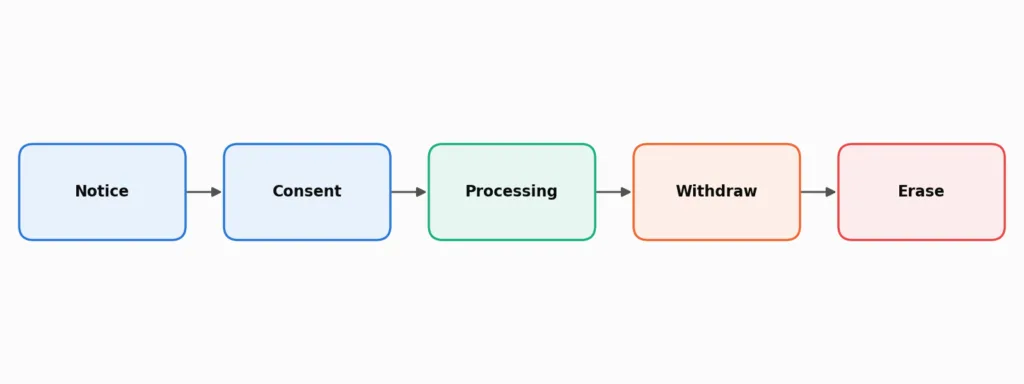
Withdrawal must be as easy as giving consent. Build it into the app settings, not only into a support email.
2. Security safeguards
Rule 6 applies from May 2027. Expect to show encryption, access control, logging of who accessed which record, and backups. Our guide to secure cloud architecture for telemedicine apps covers the technical controls.
3. Breach response with two clocks
Rule 7 requires you to inform affected users without delay and send a detailed report to the Board within 72 hours. Separately, CERT-In’s 2022 directions still require specified cyber incidents to be reported within six hours.
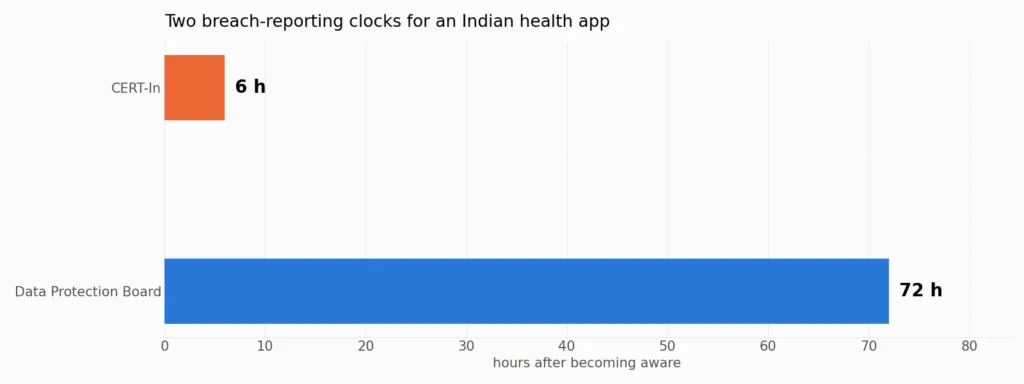
Your incident runbook should trigger both clocks from one detection event, with pre-drafted notices ready.
4. Rights requests
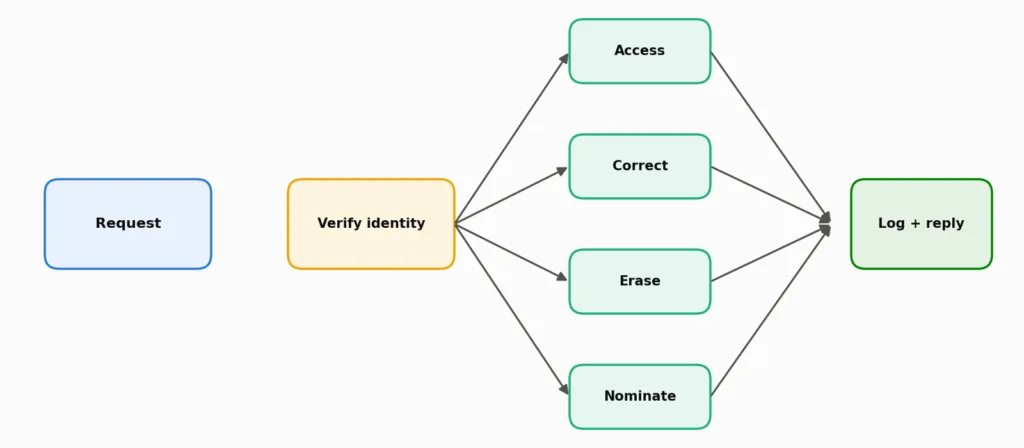
Patients can ask to access, correct or erase their data, and nominate someone to act for them. Build a request flow that verifies identity, routes to the right action and logs the reply.
Erasure in healthcare has limits. Medical records are often subject to retention rules under other laws, so erasure may mean stopping non-essential processing and deleting marketing and analytics data while keeping the clinical record for its legal period. Document that logic.
5. Children’s data
Verifiable parental consent applies to children’s data. EY’s summary notes that healthcare professionals are among the categories exempt from some parental consent requirements. Check with your lawyer exactly which exemption fits paediatric teleconsultation in your model.
6. Vendors and cross-border transfer
List every processor, what data they get and where they host it. Put contracts in place. Rule 15 covers cross-border transfers; watch for any country restrictions the government notifies.
Where DPDP meets ABDM
Many health apps also connect to the Ayushman Bharat Digital Mission. The two frameworks overlap on consent and security but are not the same.
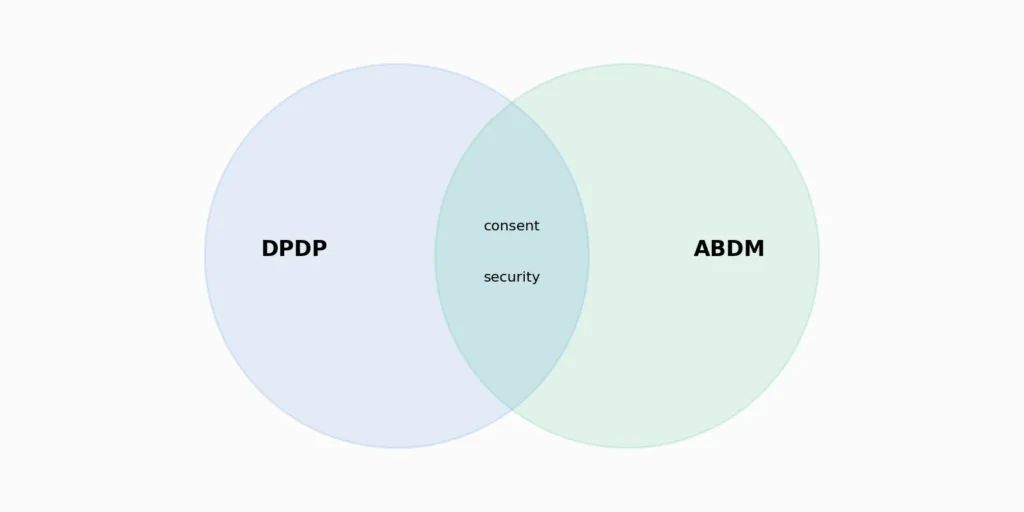
One difference matters for hosting. A 2026 legal analysis notes that the DPDP Act does not impose a blanket requirement to store health data in India, but health data processed within the ABDM ecosystem must be stored in India under the Health Data Management Policy. Most Indian health apps will find it simpler to host all clinical data in India.
Telemedicine consultations also still follow the Telemedicine Practice Guidelines from 2020 on identity, consent and prescriptions. DPDP adds to those; it does not replace them.
Penalties
The Act’s schedule allows penalties of up to ₹250 crore for failing to take reasonable security safeguards to prevent a breach. The Board decides the amount case by case.
Common mistakes
- One checkbox for everything.
Bundled consent is hard to defend. Itemise purposes. - No withdrawal button.
Withdrawal must be as easy as consent. - Only one breach clock.
CERT-In’s 6 hours and the Board’s 72 hours both apply. - Unknown processors.
Analytics SDKs and SMS gateways count too. - Treating erasure as delete-all.
Clinical retention rules still apply. - Waiting for May 2027.
The deadline may move earlier, and rebuilding consent flows takes time.
FAQ
When does the DPDP Act apply to healthcare apps?
The Rules were notified on 13 November 2025. Most obligations for health apps apply from 13 May 2027, unless MeitY notifies a shorter timeline.
Do health apps need to store data in India under DPDP?
The Act has no blanket rule, but data processed within ABDM must be stored in India, and many health apps host in India for that reason.
How fast must a health app report a data breach?
Inform affected users without delay and send a detailed report to the Data Protection Board within 72 hours. CERT-In’s 6-hour rule for cyber incidents also applies.
Is a telemedicine app a Significant Data Fiduciary?
Only if the government notifies it as one, based on factors such as data volume and sensitivity. Large platforms should prepare for it.
Sources
- DPDP Rules 2025, rule-by-rule effective dates (Gazette G.S.R. 846(E))
- EY: DPDP Rules 2025 notified by MeitY
- Cy5: DPDP Rules, 72-hour breach reporting and CERT-In
- Samisti Legal: The DPDP Act and the healthcare sector
- Medical365: Telemedicine in India guide
Related reading: Telemedicine app development guide · our article on ABHA and ABDM integration for telemedicine apps
Thanks for the feedback!
Praveen Soman CEO, Sigosoft
Technology entrepreneur and digital product strategist with a passion for building scalable software products and solving real-world business challenges. Enjoys exploring AI, emerging technologies, startups, and the ideas shaping the future of technology.
Connect on LinkedIn →Start the discussion
Questions or experiences to share? Our team reads and replies.